· Akira Agent
AI agent GDPR implementation in Sweden: DPA, data retention, and human review before go-live
A practical implementation checklist for Swedish service businesses connecting AI agents to customer data, calls, emails, CRM notes, or bookings.
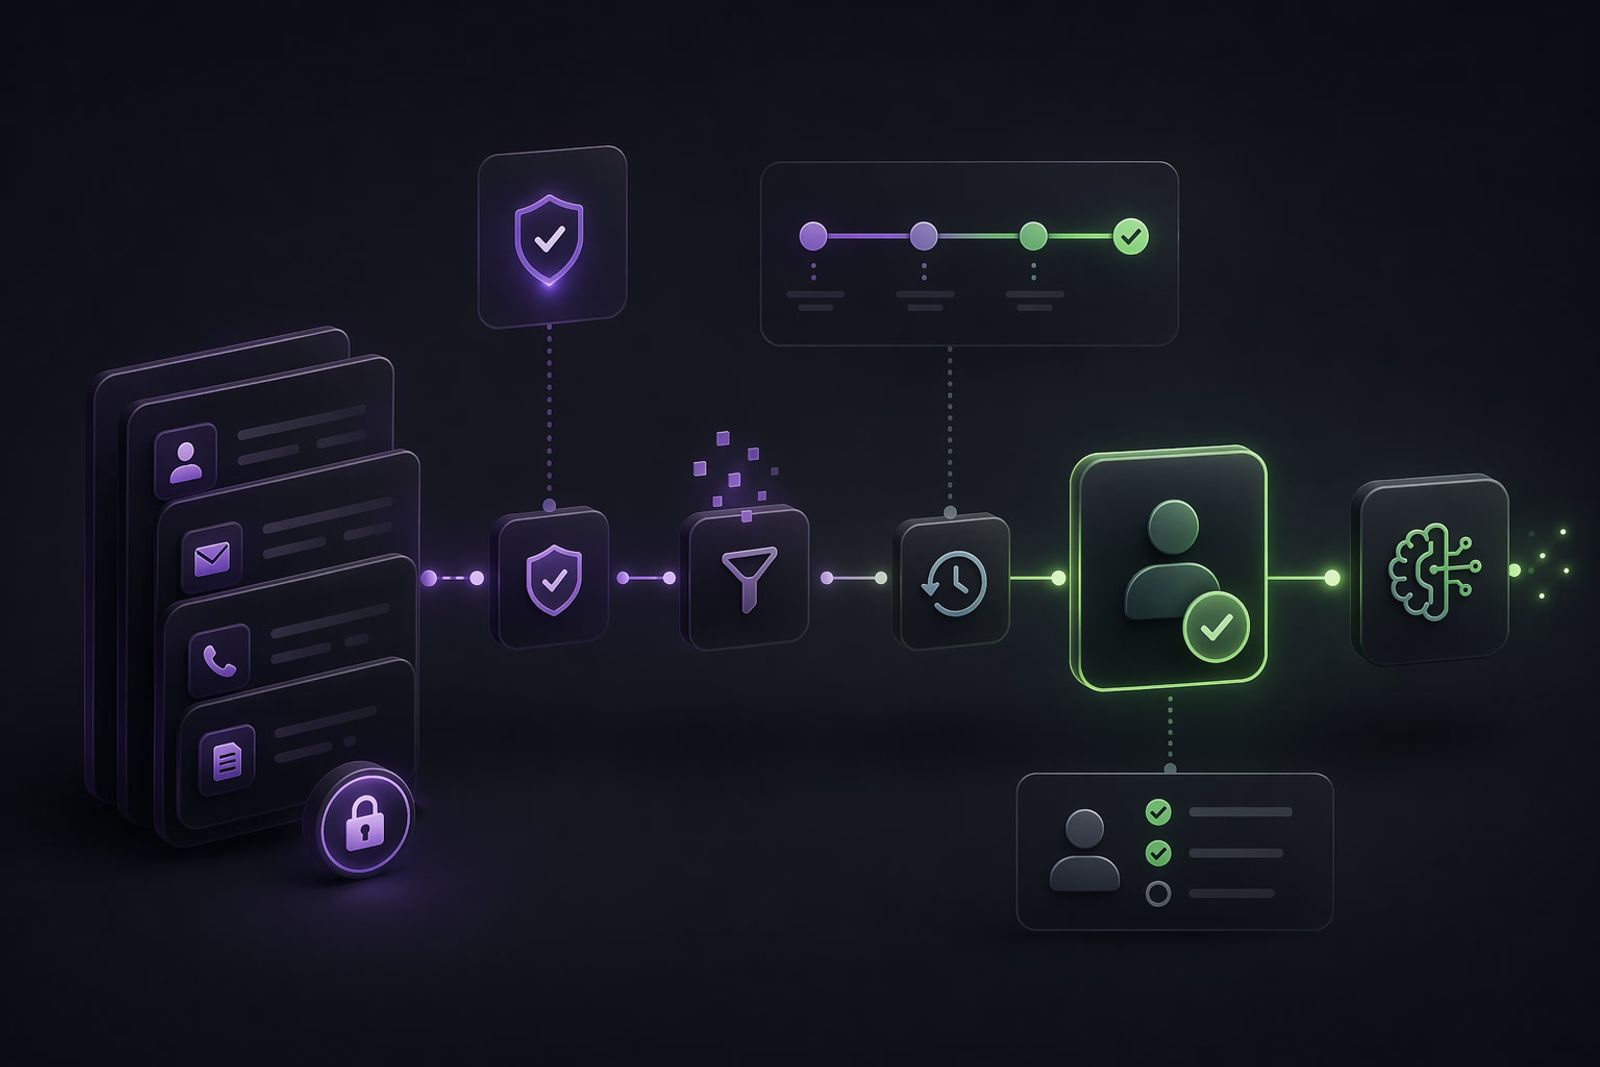
GDPR-safe AI agent implementation is not a legal slogan. It is a set of operational decisions: what data the agent sees, where that data goes, how long it is kept, who can review it, and when a human must approve the output. For Swedish service businesses, those choices should be made before the agent touches calls, emails, bookings, CRM notes, or customer follow-up.
This guide is practical, not legal advice. It is meant to help operators prepare the questions that should be answered before launch.
Map the data before choosing the tool
The first step is to list the personal data involved in the workflow. A restaurant booking may include a name, phone number, time, dietary notes, and free-text comments. A recruiter workflow may include far more sensitive candidate information. The Swedish Authority for Privacy Protection explains that GDPR applies when organisations process personal data; see IMY’s overview of what applies according to GDPR.
Decide the role of each vendor
Before launch, clarify whether vendors are processors or controllers for the data involved, and whether a data processing agreement is needed. The European Commission’s data protection overview is a useful starting point for understanding the broader EU framework. In practice, your implementation checklist should include subprocessors, retention, access control, and deletion routines.
Keep human review where judgment matters
- Complaints, cancellations with financial impact, medical or sensitive personal data, candidate rejection, and legal or contractual decisions should not be left to an unchecked workflow.
- The AI agent can draft, summarise, classify, and route. A human can approve, reject, or edit decisions that carry risk.
- Logs should make it possible to see what the agent received, what it produced, and who approved the next step.
Remember the EU AI Act context
The EU AI Act adds another layer of AI governance. The European Parliament’s overview of the EU AI Act is useful context, especially for teams using AI in areas that may require stronger controls. Most service-business workflows are not automatically high-risk, but the implementation should still be documented.
A practical launch checklist
- Define the workflow and data fields before connecting tools.
- Minimise inputs: collect only what the agent needs to perform the task.
- Set retention rules for transcripts, summaries, and CRM notes.
- Write handoff rules for sensitive cases.
- Test with synthetic or low-risk examples before using real customer data.
Akira Agent builds custom agents with these boundaries in mind. If you are deciding whether a workflow is safe to automate, start with the smallest useful version.
Book the audit
In a 30-minute audit, we can map your target workflow, data exposure, human checkpoints, and first safe automation step. Book the 30-minute Akira Agent audit.